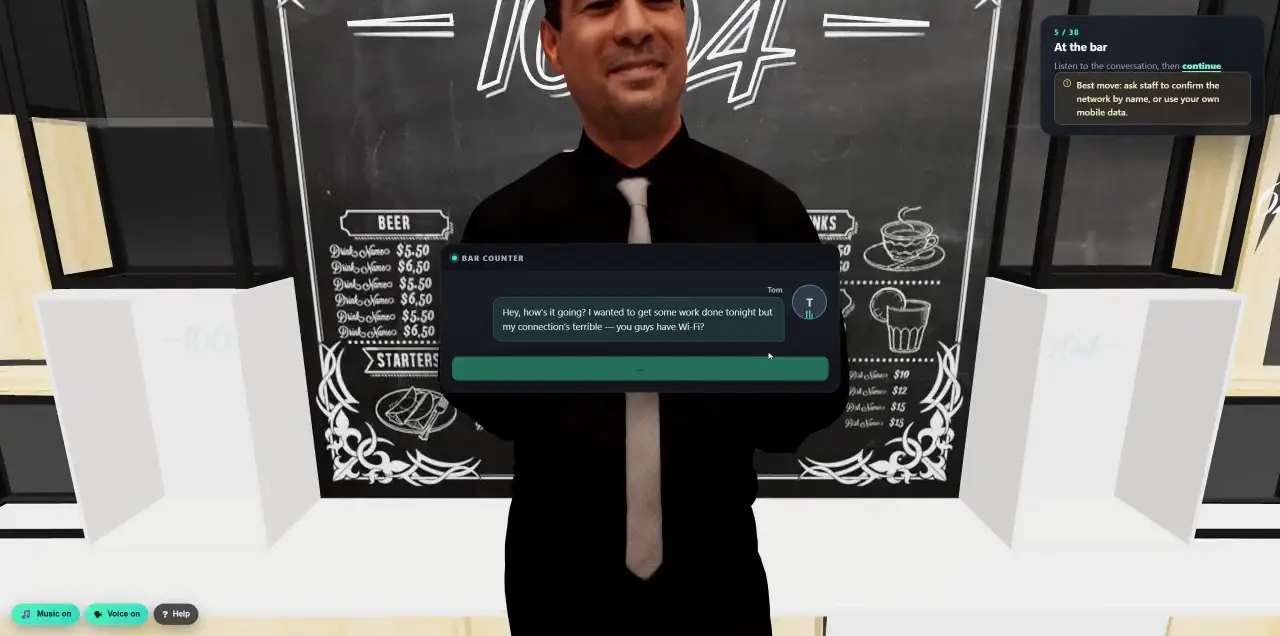
 Walk into a 3D lesson.Watch a learner go through the bar scenario, step by step.
- Industries
- MSPs and MSSPs
Security awareness training for MSPs and MSSPs, under your brand.
Your clients need awareness training, and you need it to run across dozens of tenants without eating your margin. Cyberfrog gives you one partner console, an isolated workspace per client, your brand on every screen and email, and up to 40% partner discount on list prices.
- One console, every client
- White label on every screen
- Up to 40% partner discount
- AI voice and deepfake included
Hi, I have a new phone and the authenticator app is gone. I am about to join a call with our directors and cannot wait for the ticket queue. Can you switch off MFA on my account for now? I will set it up again tonight.
Reply in chat- Identity is not verified in this channel
- Asks to switch MFA off instead of a verified reset
- Time pressure to skip the call-back procedure
Why attackers aim at the provider.
One MSP holds the keys to many clients: admin accounts, remote-management tools and a help desk that resets passwords for a living. Compromise the provider and every client is in reach, which is why your own staff need training as much as your clients do.
- Contracted help desks
Scattered Spider abuses the trusted relationships of contracted IT help desks and calls help desks to have passwords and MFA reset. CISA/FBI advisory, July 2025
- Providers as the target
Cybercriminals increasingly targeted third-party providers, such as digital services, to reach their customers. ENISA Threat Landscape 2025
- Third parties in half of all breaches
Breaches with third-party involvement rose 60% and now make up 48% of breaches. Verizon DBIR 2026
- Remote-management tools
Ransomware actors exploited an unpatched SimpleHelp RMM to compromise a software provider and its downstream customers. CISA advisory AA25-163A
Train your own team, then every client.
An MSP has two audiences: its own engineers and service desk, the most valuable target, and its clients' staff, who each need their own programme. Cyberfrog covers both from the same console.
- Your service desk
Callers posing as client users or executives who want a password or MFA reset: AI voice simulations that test your verification procedure.
- Your engineers and SOC
Fake vendor alerts, remote-access requests and codes asked for over chat, aimed at the people with admin rights across tenants.
- Client admins
Each client admin signs in on your branded page, sees only their own workspace and results, and can run campaigns or leave it to you.
- Client staff and leadership
A ready-made annual programme per client, role emails for finance, HR and IT, and management lessons for clients under NIS2 or DORA.
Every attack type, every client kept apart.
Each client runs its simulations in its own workspace, with its own sender, audience and results. Scenarios you build once in your content library can be published to the clients you choose.
- EmailThe fake supplier invoice
A fake-invoice scenario from your content library, published to the clients you choose and sent from each client's own sender.
- VoiceThe MFA reset call
An AI caller poses as a client's managing director and asks your service desk to remove MFA from an account.
- DeepfakeA client's CEO on video
A lip-synced video, used only with recorded consent and admin approval, asks finance for an urgent payment.
- ClickFixThe fake support page
A support email leads to a fake CAPTCHA that asks the user to paste a command into their computer.
Breach monitoring as a service for every client.
Darknetsearch watches leak databases, infostealer logs and hacker forums for each client's domains. When one of their people turns up, Cyberfrog sends a personal notice and assigns the matching lesson, following the training rules in that client's workspace.
It runs all year without anyone lifting a finger, feeds each person's risk score and gives you a concrete finding to discuss at every client review. Passwords are shown only as much as each client's privacy settings allow.
The rules your clients and you answer to.
Under NIS2 an MSSP can be an in-scope entity itself, and financial clients under DORA must bring their ICT providers into their training. Cyberfrog maps the frameworks it supports and gives you a branded report per client.
| Rule | What it asks for | How Cyberfrog helps |
|---|---|---|
| NIS2 Directive, Annex I (ICT service management, B2B)Mapped in Cyberfrog | Managed service providers and managed security service providers are in-scope entities, so the Art. 20 and 21 training duties apply to the provider itself. | NIS2 mapping for your own staff and for every client in scope, with coverage reports. |
| DORA, Art. 13(6) and 30(2)(i)Mapped in Cyberfrog | Financial clients must train staff, include ICT providers in their training where appropriate, and write that participation into contracts. | DORA mapping and records of your staff's participation for financial clients. |
| ISO/IEC 27001:2022, A.6.3Mapped in Cyberfrog | A common client requirement of MSSPs: information security awareness, education and training for staff. | Programme mapped to ISO 27001 and exportable evidence for your audits and your clients'. |
| UK Cyber Security and Resilience Bill | Would bring medium and large MSPs into UK NIS regulation. Introduced on 12 Nov 2025 and still in Parliament in Sep 2026; check its current status. | Training records per person, ready if the bill becomes law. |
| Five Eyes advisory AA22-131A | MSPs and their customers should review security processes and contracts; it recommends MFA, least privilege and monitoring. | Simulations that test MFA reset procedures at your service desk and at your clients'. |
Summaries for orientation, not legal advice. Cyberfrog provides training records and coverage reports; it does not certify compliance.
Questions from MSPs and MSSPs.
What is white-label security awareness training?
Training and simulations your clients see under your brand: your product name, logo and colours in the client admin, the learner portal, every email and report, and the name in authenticator apps, on your own domains. Cyberfrog stays the technology underneath, and clients cannot replace your brand.
How does the multi-tenant console work?
Each client is a separate tenant, isolated in the database. From the partner console you see the whole portfolio, step into any client as their admin, and publish your own templates to the clients you choose. Each client keeps its own campaigns and results.
How much margin is there for partners?
Partners get up to 40% discount on Cyberfrog's list prices, depending on volume and commitment. We bill you, you bill your clients at your own prices, and clients never see wholesale prices. The partner programme page has the terms.
Does NIS2 apply to managed security service providers?
NIS2 Annex I lists managed service providers and managed security service providers under ICT service management. Depending on your size and national transposition, the management and staff training duties then apply to you as well as to your clients.
Why do attackers target MSPs?
Because one provider gives access to many clients. The Five Eyes advisory AA22-131A warns about this, and groups such as Scattered Spider call outsourced help desks to have passwords and MFA reset. Training your own service desk is the first step.
Related industries.
- IndustrySaaS
Phone calls that get staff to approve a malicious connected app, stolen OAuth tokens and fake job applicants.
Read more - IndustryFinancial services
Payment-diversion emails, deepfake executives and phone calls that push staff to release a transfer or reset an account.
Read more - IndustryHealthcare
Ransomware that postpones care, help-desk calls that reset MFA, and staff who share workstations between shifts.
Read more
Add awareness to every client contract.
In a 30-minute demo we show the partner console, the white label on your own domains and a campaign in a client workspace.