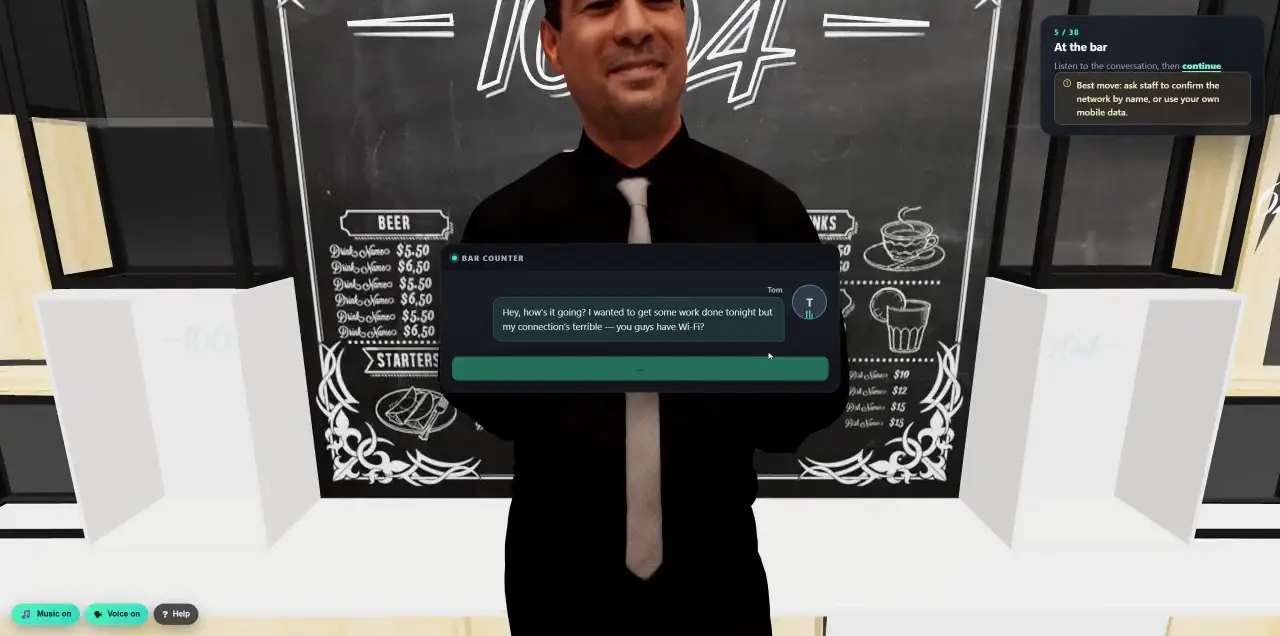
 Walk into a 3D lesson.Watch a learner go through the bar scenario, step by step.
- Industries
- SaaS
Security awareness training for SaaS companies, ready for SOC 2 and ISO 27001.
SaaS teams hold their customers' data and the keys to production, and attackers have learnt to ask for them by phone. Cyberfrog trains engineers, support, sales and leadership with simulations of the calls, chats and app approvals that really reach them, and exports the evidence your SOC 2 and ISO 27001 auditors look for.
- Vishing and app-approval simulations
- Paths for engineers, support and sales
- ISO 27001 mapping, SOC 2 records
- Events streamed to your SIEM
We are moving the CRM backup to a new export connector. Please authorise it with your account today so customer records keep syncing. Someone from the service desk will call you to walk you through the code.
Authorise connector- Asks you to grant a connected app access to customer data
- Announces a service-desk call to talk you through a code
- Sender domain is not your own identity provider
How attackers get into a SaaS company.
Attackers rarely break the product. They talk to people: a support agent who approves an app, a recruiter who hires the wrong candidate, an engineer who runs an unknown command. Each of these leads straight to customer data.
- A phone call that approves a malicious app
UNC6040 posed as IT support by phone and got employees to approve a modified Salesforce Data Loader app, then stole data and extorted the victims. Google Threat Intelligence, June 2025
- Stolen tokens through an integration
UNC6395 used compromised OAuth tokens from the Salesloft Drift integration in August 2025. The tokens were revoked on 20 August 2025. FBI FLASH-20250912-001
- Fake applicants on the payroll
North Korean IT workers hired remotely have moved on to data extortion. FBI PSA I-012325-PSA
- Shadow AI
45% of employees frequently use unapproved AI tools on corporate devices, up from 15%. Verizon DBIR 2026 release
Paths for the people with the keys to production.
An engineer with production access, a support agent who can see customer accounts and a recruiter screening remote candidates face different attacks. Each gets practice written for that work.
- Engineering and DevOps
Fake developer-platform notices, ClickFix pages that ask for a terminal command, and requests for tokens or secrets over chat.
- Customer support and success
Callers posing as customers or as your own IT team, requests to change an account owner and to approve connected apps.
- Sales, recruiting and HR
Poisoned job applications, candidates who are not who they claim to be, and invoice requests from look-alike prospects.
- Founders and leadership
Deepfake video and voice of a founder, investor-themed lures, and the Using AI safely course for teams that adopt new tools fast.
Simulate the call, not just the email.
Attacks on SaaS teams increasingly start on the phone or in chat. Cyberfrog's AI caller holds a real conversation, adapts when someone pushes back and scores the transcript, so you see exactly what was given away.
- VoiceThe IT support call
An AI caller walks a support agent through authorising a connector and asks for the code on screen.
- EmailConnected-app approval
A notice from a look-alike identity-provider domain links to a cloned sign-in page.
- ClickFixThe status-page fix
A cloned status page asks an engineer to paste a fix into the terminal to restore access.
- SMSToken expiry text
A text warns that a developer token expires today and links to a page to renew it.
Find the stealer logs before attackers use them.
Infostealer malware on a laptop or home computer captures saved browser logins, including those for code hosting, cloud consoles and admin tools. Cyberfrog checks your domains against Darknetsearch's breach and stealer-log data as often as every hour.
The person a log names gets a notice with the exact record, what to do now and a lesson on how stealers work, by email or first in Slack or Teams. Passwords are shown only as much as your privacy settings allow.
What auditors and customers ask of SaaS vendors.
SaaS vendors are asked for proof by their auditors and by customers who carry their own NIS2 and DORA duties. Cyberfrog maps the frameworks it supports and exports dated records per person for the rest.
| Rule | What it asks for | How Cyberfrog helps |
|---|---|---|
| ISO/IEC 27001:2022, clause 7.3 and A.6.3Mapped in Cyberfrog | Awareness for everyone working under the organisation's control, and information security awareness, education and training. | Programme mapped to ISO 27001, with coverage gaps flagged and evidence you can export. |
| AICPA SOC 2 Trust Services Criteria, CC1.4 and CC2.2 | Auditors map awareness training to commitment to competence (CC1.4) and internal communication of security responsibilities (CC2.2). | Dated completion records per person and exportable reports for your auditor. |
| NIS2 Directive, Annex I and II, Art. 21(2)(d)Mapped in Cyberfrog | Cloud providers and data centres are in scope, and customers' supply-chain duties flow down to their SaaS vendors. | NIS2 mapping and reports you can share in customer security reviews. |
| DORA, Art. 30(2)(i)Mapped in Cyberfrog | Contracts with ICT third-party providers must oblige the provider to take part in the financial customer's awareness programmes and resilience training. | DORA mapping and records of your staff's participation for financial customers. |
| US FedRAMP (NIST SP 800-53 AT-2) | Literacy training and awareness for staff working on systems sold to US federal agencies. | An annual programme and per-person records for your AT-2 evidence. |
Summaries for orientation, not legal advice. Cyberfrog provides training records and coverage reports; it does not certify compliance.
Questions from SaaS teams.
Does SOC 2 require security awareness training?
SOC 2 does not name a specific course, but auditors map awareness training to criteria CC1.4 (commitment to competence) and CC2.2 (communicating security responsibilities). Most companies therefore train at onboarding and at least once a year, and keep a record per person.
What are the ISO 27001 awareness training requirements?
ISO/IEC 27001:2022 covers awareness in clause 7.3, and Annex A control 6.3 covers information security awareness, education and training. Cyberfrog maps its lessons to these and shows gaps before you publish the programme.
What does DORA require from ICT providers?
DORA Art. 30(2)(i) says contracts between financial entities and ICT third-party providers must include the provider's duty to take part in the financial entity's ICT security awareness programmes and resilience training. If you sell to banks or insurers in the EU, expect that clause.
What training evidence can we give auditors?
Who was trained on what and when, and how people did in simulations. Cyberfrog exports a one-page executive summary, a full report, an editable Word document and a CSV of every recipient and event.
Can we simulate more than phishing email?
Yes. AI voice calls in 28 languages, SMS, deepfake video, MFA prompts, ClickFix pages and multi-stage conversations, each followed by a short lesson on the exact trick used.
Related industries.
- IndustryMSPs and MSSPs
Attackers go after the provider to reach every client behind it, from the outsourced help desk to the remote-management tools.
Read more - IndustryFinancial services
Payment-diversion emails, deepfake executives and phone calls that push staff to release a transfer or reset an account.
Read more - IndustryLegal
Fake IT-support callers, diverted client payments and ransomware aimed at the confidential files every firm holds.
Read more
Pass the audit, stop the phone call.
In a 30-minute demo we show the vishing, app-approval and ClickFix simulations and the evidence exports, on your own domain.