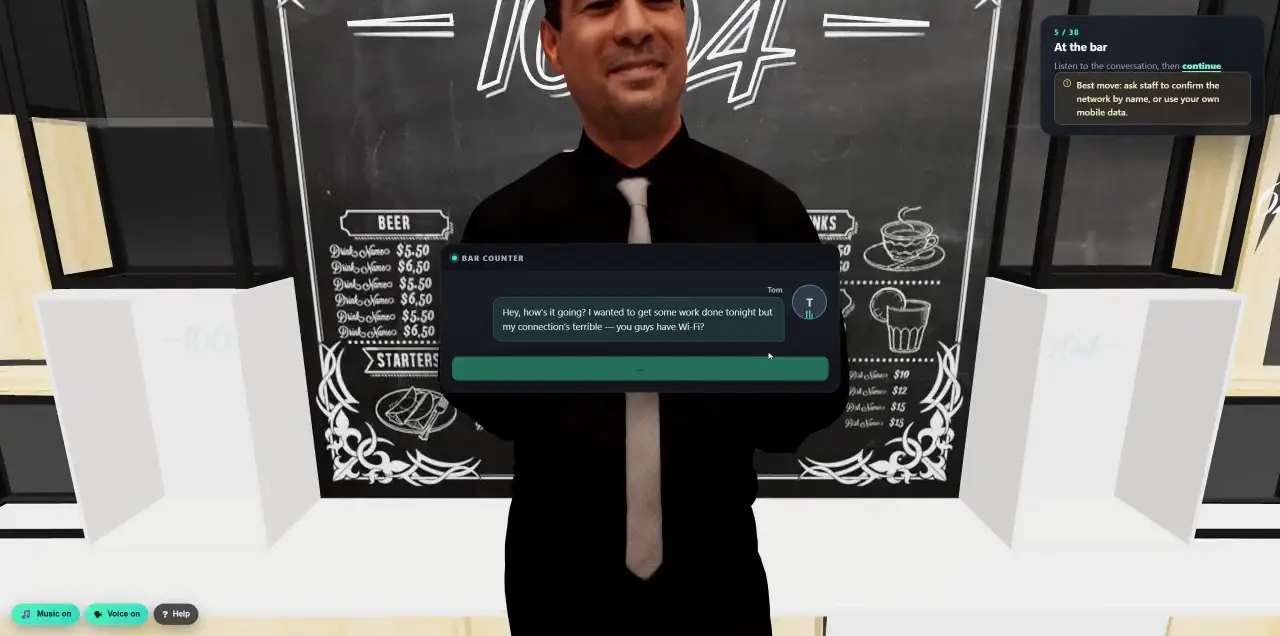
 Walk into a 3D lesson.Watch a learner go through the bar scenario, step by step.
- Industries
- Manufacturing
Security awareness training for manufacturing, from the office to the shop floor.
When a plant stops, every hour costs output, deliveries and customer trust. Cyberfrog trains shift teams, purchasing, engineering and management with short lessons and simulations of the supplier and support lures they really receive, and keeps the records NIS2, TISAX and your customers ask for.
- Short lessons for shift teams
- Supplier, invoice and vishing simulations
- Posters for the shop floor
- NIS2 and ISO 27001 mapping
Following an audit of our banking arrangements, all payments must go to our new account from this week. Please update your vendor record before Friday's payment run. Payments to the old account will be returned and may delay your next delivery.
View new bank details- Domain differs slightly from the supplier's usual one
- Bank change announced by email only, no call from a known contact
- Threatens late deliveries to rush the payment run
How attackers stop a production line.
Manufacturers rely on just-in-time supply, long supplier lists and IT that reaches into production. Attackers come in through a supplier, an invoice or a call to the service desk, then hold the downtime to ransom.
- Europe's most consistently targeted sector
Across the five EU member states named most often in ransomware claims, manufacturing was the most consistently targeted sector. ENISA Threat Landscape 2025
- Top of the incident-response caseload
Manufacturing made up 27.7% of IBM X-Force incident-response cases in 2025, more than any other industry. Manufacturing Dive on IBM X-Force 2026
- Suppliers as the way in
In manufacturing, a third party is involved in 61% of breaches and the human element in 56%. Phishing accounts for 13% of initial access. Verizon DBIR 2026
- A shutdown felt nationally
After the 2025 cyberattack on Jaguar Land Rover, the UK government backed a loan guarantee of up to £1.5 billion. GOV.UK, September 2025
One plant, four very different risks.
A machine operator on a shared terminal, a buyer paying suppliers and an engineer with remote access to the line each face different attacks. Cyberfrog gives every group practice written for its job.
- Production and shift teams
Shared terminals, USB sticks and QR codes, for people who rarely read email: five-minute lessons, posters by the line and texts for those with a work phone.
- Purchasing, finance and sales
Changed bank details, fake suppliers and spoofed customer orders, with Verify before you pay for everyone who approves payments.
- Engineering, IT and OT
Fake vendor support calls, remote-access tool requests and urgent admin alerts aimed at people who can reach production networks.
- Management and the board
Deepfake calls from the managing director, plus the regular management training NIS2 and BSIG §38(3) require of in-scope manufacturers.
The supplier email, without the real loss.
Simulations copy the requests a plant really receives, from suppliers' finance teams to machine vendors' support desks. A mistake leads straight to a short lesson; a report goes to your security team and counts in the results.
- EmailNew bank details from a supplier
A look-alike supplier domain asks accounts payable to update the vendor record before the payment run.
- VoiceThe machine vendor's support line
An AI caller from a fake service partner asks an engineer to install remote-support software for a firmware fix.
- QRThe canteen poster
A QR code on a poster leads shift staff to a cloned sign-in page for the roster portal.
- Multi-stageThe customer who writes back
An email conversation about a large order builds trust over several replies before sending a link to a fake file share.
Find the leaked logins before they reach the plant.
Remote access, supplier portals and engineering tools are often protected by a single password, and that password leaks through breaches and infostealer malware on home or shared computers. Cyberfrog checks your domains against Darknetsearch's breach and stealer-log data and raises the risk score of each person a finding names.
Fresh stealer logs and reused passwords weigh most. The person gets a notice on what was found and a lesson on how it happened, so a leaked VPN or portal login is changed before an attacker tries it. Passwords are shown only as much as your privacy settings allow.
What rules and customers ask of manufacturers.
Manufacturers answer to NIS2 and to their customers' supplier requirements, from TISAX in automotive to IEC 62443 in industrial automation. Cyberfrog maps the frameworks it supports and keeps a record per person for the others.
| Rule | What it asks for | How Cyberfrog helps |
|---|---|---|
| NIS2 Directive, Art. 20 and 21 (manufacturing, Annex II)Mapped in Cyberfrog | Makers of medical devices, electronics, electrical equipment, machinery, motor vehicles and other transport equipment are in scope; management training and cyber-hygiene training apply. | NIS2 mapping, management lessons and coverage reports you can export. |
| Germany, BSIG §38(3) | Regular training for the management of in-scope manufacturers. | Management lessons and a dated record for each leader. |
| TISAX / VDA ISA | The VDA ISA catalogue assessed under TISAX includes controls on employee awareness and training. | Role paths and completion records to show in a TISAX assessment. |
| ISA/IEC 62443-2-1 | Security programme requirements for industrial automation asset owners, including personnel training and awareness. | Simulations aimed at engineering and OT staff, with training records per person. |
| ISO/IEC 27001:2022, clause 7.3 and A.6.3Mapped in Cyberfrog | Awareness for everyone working under the organisation's control, and information security awareness, education and training. | Programme mapped to ISO 27001, with coverage gaps shown before you publish. |
| US CMMC (32 CFR 170) and NIST SP 800-171 | Defence suppliers handling controlled unclassified information must meet the Awareness and Training requirement family. | An annual programme with per-person records; the CMMC assessment remains your own. |
Summaries for orientation, not legal advice. Cyberfrog provides training records and coverage reports; it does not certify compliance.
Questions from manufacturers.
Is TISAX awareness training required?
The VDA ISA catalogue that TISAX assessments use includes controls on employee awareness and training. It does not prescribe a course, so assessors look at whether staff are trained and how you prove it. Cyberfrog provides role paths and completion records; it does not issue a TISAX label.
What does IEC 62443 say about training?
IEC 62443-2-1 sets security programme requirements for industrial automation asset owners, including training and awareness for personnel. Cyberfrog covers the human side, such as phishing, fake support calls and remote-access requests aimed at engineers. It does not replace technical OT security.
How do you train shop-floor staff who rarely use email?
With five-minute lessons that run on any device, posters for the line and the canteen, and text and voice simulations for people with a work phone, each in the person's own language.
Does NIS2 apply to manufacturers?
NIS2 Annex II lists makers of medical devices, electronics, electrical equipment, machinery, motor vehicles and other transport equipment, as well as chemicals. Company size and national transposition decide whether you are in scope. In Germany, BSIG §38(3) also requires regular management training.
Does CMMC require security awareness training?
Yes. Defence suppliers handling controlled unclassified information must meet the Awareness and Training requirement family of NIST SP 800-171, which CMMC (32 CFR 170) assesses.
Related industries.
- IndustryLogistics
Fake load-board listings, remote-access tools that end in stolen cargo, and ransomware that stops transport.
Read more - IndustryFinancial services
Payment-diversion emails, deepfake executives and phone calls that push staff to release a transfer or reset an account.
Read more - IndustryPublic sector
Calls posing as the authorities, AI voice messages from senior officials and ransomware that stops municipal services.
Read more
Keep the line running.
In a 30-minute demo we show the supplier, invoice and vishing simulations for office and shop-floor teams, on your own domain.